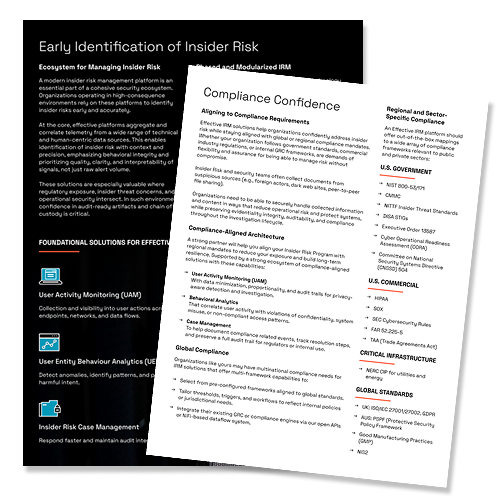
Achieve CORA-Compliant Insider Risk Monitoring
Trusted Visibility. Audit-Ready Evidence. Mission-Ready Compliance
Achieve Cyber Operational Readiness Assessment (CORA) compliance with insider risk monitoring designed for government, defense and the Defense Industrial Base (DIB). Everfox provides privileged user monitoring, keystroke monitoring, file shadowing and comprehensive forensic evidence to help organizations strengthen insider risk programs and produce audit-ready evidence.
.png)
Organizations are expected to demonstrate continuous monitoring, visibility into priviledged user activity and defensible evidence that supports investigations and compliance.
Many organizations struggle to achieve these requirements because monitoring capabilities are fragmented across multiple tools, investigations rely on incomplete evidence and security teams lack a consistent view of user activity across the enterprise.
Everfox helps organizations build a connected insider risk management program that aligns with the U.S. Department of War's Cyber Operational Readiness Assessment (CORA) requirements while reducing operational complexity.
A Practical Guide for Evaluating Insider Risk Tools for their Ability to Surface Early Indicators and Eliminate Blind Spots.
Download
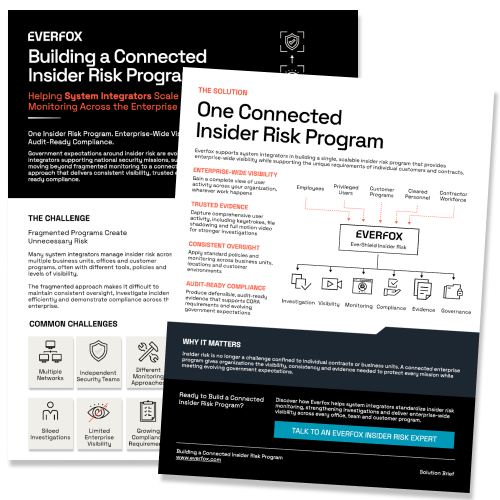
Helping System Integrators Scale Insider Risk Monitoring Across the Enterprise.
Download
Explore how organizations can rethink insider risk in an environment where users, systems, and AI agents increasingly interact with sensitive information.
Watch HereSecurity teams struggle to monitor privileged users and identify suspicious activity before it becomes mission risk.
Producing complete evidence packages for investigations and audits is often manual, time consuming and inconsistent.
Multiple tools create gaps in visibility, inconsistent reporting and increased operational overhead.
Gain Visibility Into Privileged User Activity
Monitor user activity across critical systems with comprehensive visibility into users, applications and system interactions.
Capture Trusted Evidence
Record detailed user activity, including keystrokes, file shadowing and full motion video, providing investigators with comprehensive forensic evidence that supports audits and incident response.
Build Audit-Ready Programs
Generate consistent, defensible evidence that helps organizations demonstrate compliance while reducing the time and effort required for CORA or other compliance assessments.
Protect Mission Continuity
Detect, investigate and respond to insider risk without disrupting mission-critical operations.
Standardize Insider Risk Monitoring
Establish a consistent approach to insider risk across business units, customer programs and security teams.
Accelerate Insider Risk Investigations
Reduce investigation time with comprehensive forensic evidence that provides the context needed to understand user activity. From privileged access to file interactions and user sessions.
Simplify Compliance Reporting
Replace fragmented evidence collection with centralized monitoring and consistent reporting.
One Insider Risk Program. Enterprise-Wide Visibility
Large system integrators shouldn't have multiple disconnected insider risk programs operating across different business networks and customer environments. Everfox helps organizations created a connected enterprise strategy that delivers standardized monitoring, trusted evidence and consistent compliance enterprise wide.
See how to build a connected insider risk program >
Modern insider risk programs require continuous visibility, not periodic compliance checks. Everfox provides real-time user activity monitoring and behavioral insights that help security teams identify and respond to risk before it impacts mission operations, enabling organizations to move beyond compliance toward operational resilience.
Everfox supports threat-informed defense by providing visibility into user behaviors associated with common adversary tactics and techniques, including Privilege Escalation (TA0004), Lateral Movement (TA0008) and Exfiltration (TA0010). This enables security teams to investigate suspicious activity with greater context and confidence
Identifying risky behavior before it becomes an incident is critical to reducing organizational risk. Everfox helps security teams detect unauthorized software usage, excessive privilege, policy violations and other high-risk user activity, enabling organizations to reduce their attack surface before it can be exploited.
Every user leaves a behavioral footprint. Everfox establishes behavioral baselines and provides comprehensive user activity visibility to help organizations identify Key Indicators of Risk (KIORs), such as unusual access patterns, off-hours activity, credential misuse and abnormal data access. By surfacing these indicators early, security teams can prioritize investigations and respond before insider risk becomes mission impact
Insider Risk isn't new to Everfox, for decades, we've helped national security organizations, government and defense agencies, intelligence communities and critical services monitor, investigate insider threats and protect mission-critical environments.
Rather than adapting commercial monitoring tools for government, Everfox delivers capabilities proven in some of the world's most demanding security environments.
Everfox UAM goes beyond detection with a more pro-active and operationally proven approach to mitigating insider risk.
Learn More
Everfox UBA provides powerful behavioral insights to analysts so they can rapidly respond to risky behaviors before it’s too late.
Learn More
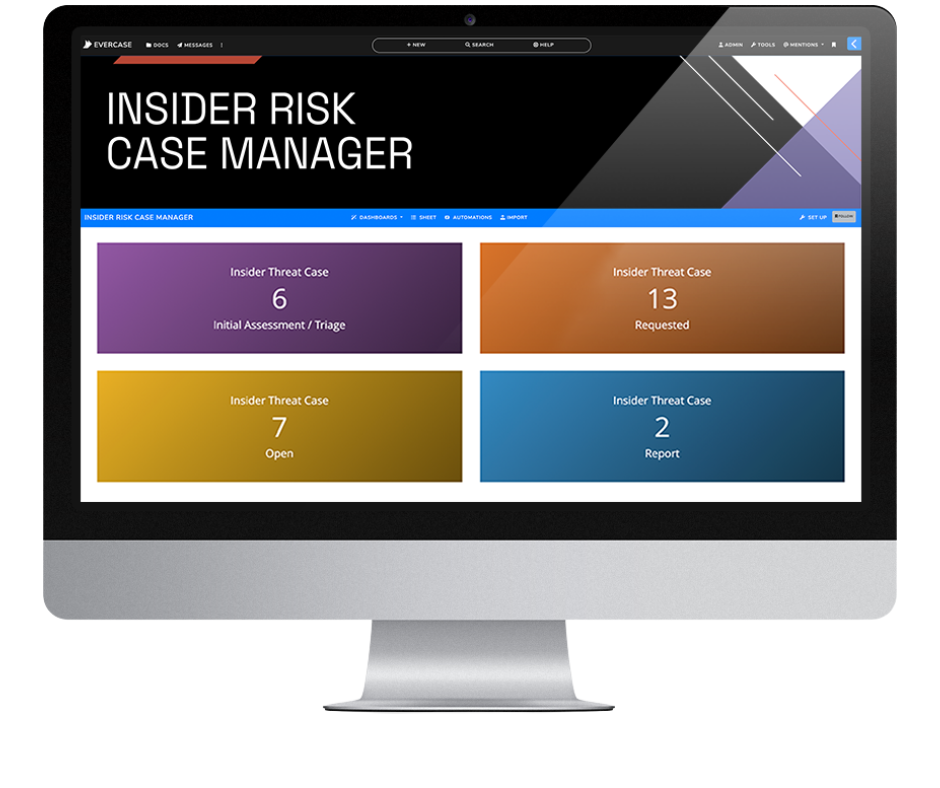
Everfox Insider Risk Case Manager software centralizes evidence, artifacts, and documentation. In-app messaging + systematic workflows help you collaborate with your team to manage more cases with greater confidence.
Learn MoreWhat is CORA Compliance for Insider Risk?
CORA establishes requirements for organizations to strengthen insider risk programs by improving visibility into user activity, monitoring privileged access and maintaining evidence that supports investigations and compliance assessments.
Organizations must demonstrate they can identify, investigate and respond to insider risk while maintaining operational continuity.
Who Needs to Comply with CORA Insider Risk Requirements?
CORA requirements primarily apply to government organizations and are increasingly influencing expectations for Defense Industrial Base (DIB) organizations, system integrators and contractors that support government missions.
Any organization handling sensitive government information or operating within national security environments should be prepared to demonstrate mature insider risk monitoring capabilities.
How Can Organizations Meet CORA Insider Risk Requirements?
Meeting CORA requirements requires more than implementing a single monitoring tool. Organizations need continuous visibility into user activity, effective monitoring of privileged users, comprehensive forensic evidence and consistent processes that support investigations and compliance audits.
A connected insider risk program helps security teams maintain oversight while reducing operational complexity.
What is Privileged User Monitoring?
Privileged user monitoring is the continuous observation and recording of activity performed by users with elevated permissions, such as administrators, system operators and other at risk accounts. Monitoring privileged users helps organizations detect suspicious behavior, investigate incidents and reduce the risk of unauthorized access to critical systems and sensitive information.
How do Keystroke Monitoring and File Shadowing Support Insider Risk Investigations?
Keystroke monitoring records users input while file shadowing captures file activity, providing investigators with detailed context around user actions. Together, these capabilities help security teams understand what occured, reconstruct events and produce the evidence needed to support investigations and compliance reviews.
How Does Everfox Help Organizations Achieve CORA-Compliant Insider Risk Monitoring?
Everfox helps government agencies, DIB organizations and system integrations build insider risk programs that support CORA compliance through comprehensive UAM, privileged user visibility and audit-ready forensic evidence. With capabilities including keystroke monitoring, file shadowing and full motion video recording.
Why Do Government Agencies and System Integrators Choose Everfox for Insider Risk Management?
For decades, Everfox has supported national security organizations with trusted insider risk management solutions in some of the world's most demanding environments.
Everfox's experience protecting government missions, combined with comprehensive forensic evidence and privileged user monitoring capabilities, enables organizations to strengthen insider risk programs with confidence while meeting evolving compliance requirements.